わたしのブログサーバ(Alibaba Cloud ECS の仮想マシン)に“Unusual logon activity detected”があったと通知がありました。 日本語に訳すと”不審なログイン(サインイン)活動が検出されました”。
結論をいうと意図的で計画的なものではあるのですが、Alibaba Cloud の Security Center を使っているこういう便利なセキュリティアラートが提供されています、という紹介です。
目次
どんな時に発生するセキュリティアラートなのか?
Alibaba Cloud 上の仮想マシンにいつもと異なる方法でログインされたときに警告がはっせられます。 今回はいつもと異なる接続元IPアドレスからの SSH 接続を契機としています。
旅行に行っていたのですが、旅先でブログのタイトルに明らかな誤字があることがわかり修正しようと考えました。修正のためには WordPress の管理画面へのアクセス制限を解除する必要があり、そのためにはまずは 以下の操作を行いました。
- Alibaba Cloud コンソールにログイン
- Securtiy Group でSSH接続元IPアドレスを追加
- SSH接続
- .htaccess を編集
- WordPressにログインし記事を修正 この一覧のアクティビティの中で
今回のセキュリティアラートは3つ目の SSH 接続で普段と違うIPから接続されたということで警告を出してくれたようです。いわゆるなりすましログインのリスクの予兆となります。
セキュリティアラートの見え方
セキュリティアラートは何か所かで確認することができます。 順番に紹介します。
Eメールでセキュリティアラートを確認することが可能です。
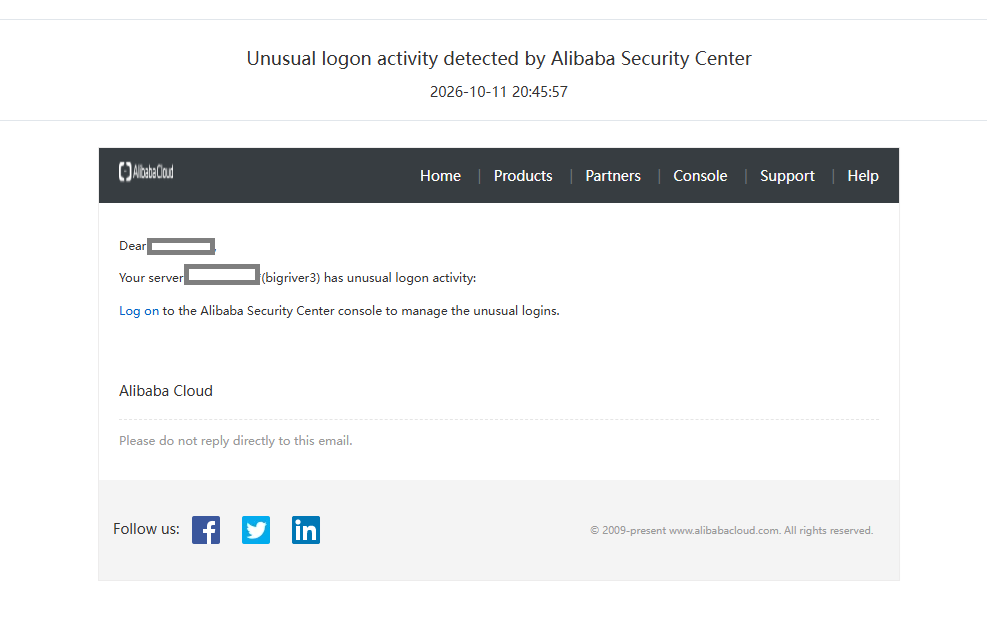
Subject : Unusual logon activity detected by Alibaba Security Center
コンソールのMessage Center からも確認可能です
メッセージの中にメールで案内されたものと同じ内容を確認可能です。
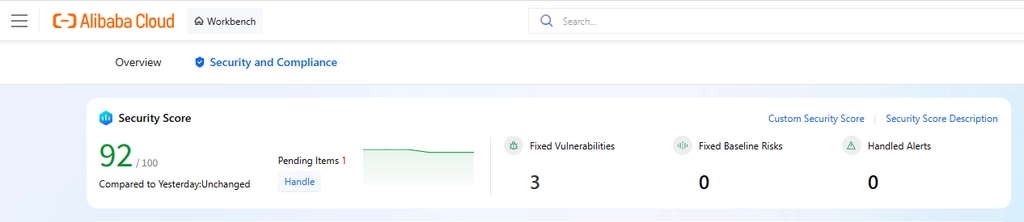
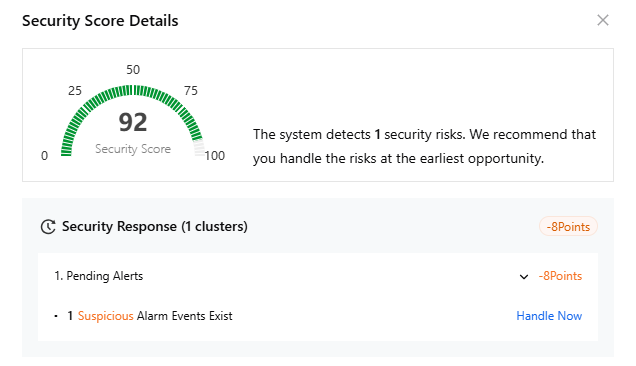
不審なログインは Security Center のスコアにも影響します。 ”-8″点減点されて 92点になっています。
Score をブレイクダウンすると -8 Pointsとして “1 Suspicious Alam Evnts exist” が確認できます。
さらにブレイクダウンするとより詳細な情報も確認可能です。
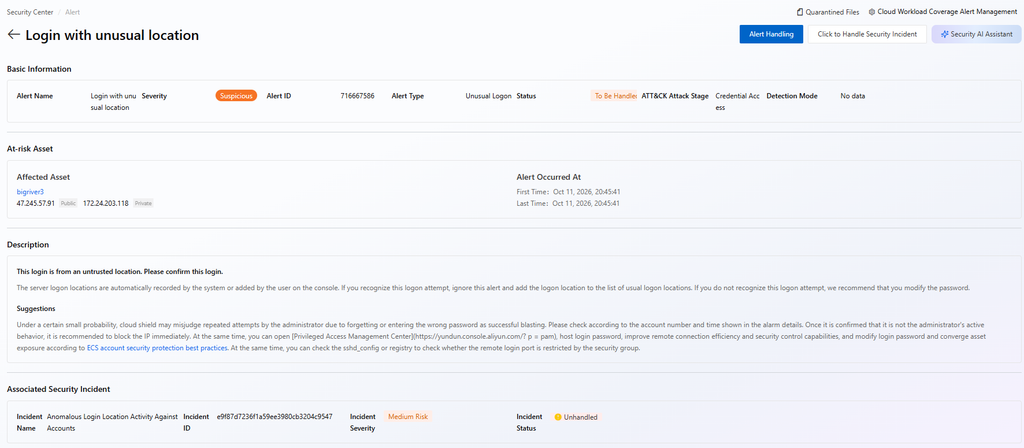
Description セクションとして詳細に発生原因や対処方法などが案内されます。 今回とは直接関係しないですが PAM ツールも提供されていることが新たにわかりました。 今度試してみるリストに追加しておきます。
This login is from an untrusted location. Please confirm this login.
The server logon locations are automatically recorded by the system or added by the user on the console. If you recognize this logon attempt, ignore this alert and add the logon location to the list of usual logon locations. If you do not recognize this logon attempt, we recommend that you modify the password.
Suggestions
Under a certain small probability, cloud shield may misjudge repeated attempts by the administrator due to forgetting or entering the wrong password as successful blasting. Please check according to the account number and time shown in the alarm details. Once it is confirmed that it is not the administrator’s active behavior, it is recommended to block the IP immediately. At the same time, you can open [Privileged Access Management Center](https://yundun.console.aliyun.com/? p = pam), host login password, improve remote connection efficiency and security control capabilities, and modify login password and converge asset exposure according to ECS account security protection best practices. At the same time, you can check the sshd_config or registry to check whether the remote login port is restricted by the security group.
実施した対処
今回のセキュリティアラートについては私が意図した操作によるものなので、Securit Center上では問題なしとして対処済しました。
以上